

Authenticator App - 2FA
Authenticator 2FA Lab
- 3.9
- 128.00 Reviews
- 1.00M
- Downloads
- Free
- Price
Screenshots
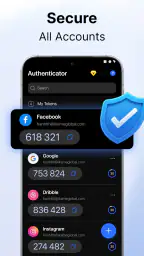
Authenticator App - 2FA Pros and Cons
Pros
- Supports multiple accounts in one place
- Works offline after codes are initially configured
- Simple interface makes code access quick
- Can help protect accounts from password theft
- Compatible with many services using standard 2FA
Cons
- Losing the device can make account recovery difficult
- Some features may require a premium upgrade
- No built-in way to recover every deleted token
- Manual setup can be confusing for first-time users
- You still need backup codes for safer account recovery
 Analysis by All-app
When I first opened Authenticator App - 2FA, I approached it with a simple goal: add a second layer of protection to the accounts I use every day without turning every sign-in into a project. That is the right way to understand this productivity app from Authenticator 2FA Lab. It is not a password manager, a security dashboard, or a replacement for your account provider. Its job is narrower and useful: it generates the temporary verification codes required by services that support two-factor authentication.
The app is free to install, aimed at Everyone, and has reached more than a million installs. Its average rating sits at 3.9 from roughly ten thousand ratings, so the overall picture is positive but not flawless. I found that fair. The basic idea is easy to understand, and the central task can be completed quickly, but the quality of the experience depends heavily on how carefully you handle the first setup and how prepared you are for losing access to the phone.
From an unprotected account to a working second step
I start with the account I want to protect, because installing an authenticator alone does not activate a second step. This section follows the handoff from an account’s security settings to a code the service accepts, with particular attention to checking that the connection works before relying on it. A careful first setup also makes later sign-ins easier to manage.
Starting with the account that needs protection
The most useful starting point is not installing the app at random. I recommend beginning inside the security settings of one account you genuinely want to protect, such as an email account, social profile, shopping account, or work service. Look for its two-factor authentication option and choose the method based on an authenticator application. The service normally presents a QR code or a setup key. That is the handoff where this app becomes useful.
This order matters because the authenticator does not decide which accounts to secure for you. The account provider creates the connection, while the app stores the information needed to produce the changing code. If you open the app first without having a service ready, you may understand the interface but still have nothing meaningful to add. Starting from the account makes the workflow clearer and reduces the chance of enabling a security method without knowing how you will finish it.
I also suggest choosing an account where you can complete the entire process in one sitting. Email is often a sensible first choice because it can be used to recover other accounts, but that also makes it especially important to save any recovery codes offered by the service. Those recovery codes are not the same as the rotating codes shown by the authenticator, and confusing the two can leave you stuck later.
Adding the account without rushing the handoff
Once the provider displays its setup code, move to Authenticator App - 2FA and use the option for adding an account. The practical choice is whether to scan the QR code or enter the setup key manually. Scanning is usually faster when the QR code is displayed on another screen. Manual entry is more useful when the setup page is on the same phone, when the camera has trouble reading the image, or when privacy-conscious users prefer not to point the camera at a screen.
More Reads From Our News Desk

Switching to the Xbox App: What Changes in Your Gaming Routine

Coloring & Learn Review: A Satisfying Canvas, Cluttered Menus

Microsoft 365 Copilot on Your Phone: Who Actually Needs It?

Mafia City: The Crime Saga That Outshines Its Rivals

Woodturning Transformed: How OS Updates Enhance Your Craft

How Tiles Hop EDM Rush Redefines Music Gaming
This is one of the first places where patience pays off. A setup key is easy to mistype, and one incorrect character can create codes that look perfectly normal but never work. If manual entry is necessary, I check the account label and key carefully before saving. If scanning is available, I still verify that the new entry is clearly associated with the correct service. A vague label may be manageable with one account, but it becomes confusing when several entries accumulate.
The app’s role at this stage is deliberately focused. It gives you a place to create and read the verification code, while the service you are securing remains responsible for confirming that the code is correct. That division can feel slightly fragmented to a first-time user, but it is also why the process works across many unrelated services instead of being tied to one company.
Confirming the first code
After the account is added, the app displays a time-sensitive code. Return to the service’s setup screen, type the current code, and confirm the change. I found this step less intimidating than it sounds, but timing still matters. If the code is close to changing, I prefer to wait for the next one and enter it promptly rather than trying to finish with only a few seconds remaining.
The important result is not merely seeing a code in the app. The account provider must accept it and complete the activation. Until that confirmation succeeds, the second factor is not reliably in place. This is also the moment to save the provider’s recovery codes somewhere safe, separate from the phone itself. If the phone is lost, damaged, reset, or unavailable, the recovery route may be the difference between a minor inconvenience and a locked account.
For a realistic everyday example, imagine signing into an email account from a new laptop at home. You enter the password on the laptop, open the authenticator on your phone, read the current code, and type it into the laptop. The handoff is simple because each device has a clear role: the laptop requests access, the phone supplies the second proof, and the email provider decides whether both pieces match.
Using it during an ordinary sign-in
Once several accounts are added, the app becomes more of a quick reference tool than a setup wizard. I open it, identify the service, read the current code, and return to the sign-in screen. The process is familiar after a few attempts, but it does introduce a small interruption compared with a password-only login. That interruption is the trade-off: a stolen password alone is less useful when the attacker also needs the temporary code.
Labels become surprisingly important here. If you use more than one account with the same provider, distinguish them clearly when adding them. A label that includes the account’s purpose or address is more helpful than a generic name. This is a small organizational habit, but it prevents the most common human error in a multi-account authenticator: copying a valid code from the wrong entry.
I would also avoid deleting an old entry just because you are changing phones or cleaning up the list. First make sure the replacement setup works, then remove the obsolete item only when you are confident it is no longer needed. The code is tied to the account’s setup relationship, not simply to the name displayed in the app.
Where the handoffs create friction
The workflow crosses several boundaries: the account’s security page, the authenticator, the device displaying the QR code, and sometimes a recovery process. Every handoff creates an opportunity for confusion. A user may assume that installing the app automatically protects an account, when in reality protection begins only after the account provider accepts the first code.
Another awkward situation occurs when the QR code is shown on the same phone where the authenticator is installed. In that case, scanning is not always the natural option. Manual setup becomes the fallback, and it demands more care. I consider this a limitation of the general workflow rather than a reason to dismiss the app, but newcomers should know that the smoothest path usually involves a second screen.
There is also a human handoff between the person setting up the account and the person later signing in. If you configure an account for a family member or help a colleague, make sure the person who will actually need the codes understands which device holds the authenticator and where the recovery method is stored. Leaving that knowledge with the installer creates a fragile arrangement.
What the app does well in the complete flow
In my experience, the strongest part of Authenticator App - 2FA is its focused purpose. It does not ask me to reorganize all my passwords before I can protect one account. I can add a service when I need it, read a code during login, and return to whatever I was doing. That makes it approachable for someone moving away from text-message verification or adding two-factor authentication for the first time.
Its free availability also lowers the barrier to trying this security method. The app supports devices running Android 7.0 or later, which covers a broad range of phones. The current version is 1.0.18, and the app’s age rating of Everyone makes its intended audience straightforward: ordinary users who need a practical security utility rather than a specialist tool.
The developer, Authenticator 2FA Lab, has kept the concept recognizable. If you already understand how time-based verification works, there is little conceptual overhead. If you do not, the most important lesson is easy to retain: your password is one proof, and the temporary code is another proof generated from the account’s setup information.
Three habits that make the experience safer
First, I treat setup as a two-part task: connect the account, then test a real sign-in before closing everything. This catches a wrong label, a mistyped key, or an incomplete activation while the original security page is still available. Testing immediately is more useful than assuming success because an entry appears in the app.
Second, I keep recovery information outside the phone. The authenticator can provide the code needed for normal access, but it should not be the only path back into the account. A phone can be lost, reset, or unavailable during travel. Saving recovery codes securely before an emergency is one of the most valuable steps in the entire workflow, even though it happens on the account provider’s side rather than inside the authenticator.
Third, I use a deliberate naming system for multiple entries. For example, I separate personal and work accounts instead of relying on a service name alone. This is not a flashy feature, but it improves accuracy when several codes are changing at once. It also makes the app more usable for people who manage accounts for a household or small team without mixing identities.
How it compares with the usual alternatives
Compared with receiving codes by text message, an authenticator app is less dependent on mobile network availability and does not require a message to arrive before signing in. That can be valuable while traveling or in places with unreliable reception. The cost is that the phone itself becomes more important, so recovery planning matters more.
Compared with a password manager that also generates verification codes, this app is more narrowly focused. Someone who wants one place for passwords, secure notes, autofill, and one-time codes may prefer an established password manager. On the other hand, a user who already has a password system and only needs a separate code generator may appreciate the simpler division.
Compared with hardware security keys, the app is easier to start with because it does not require carrying another physical object. A security key can be a stronger fit for people facing serious account-targeting risks or managing high-value professional access, while this app is more convenient for everyday accounts. Convenience is its advantage, but it should not be mistaken for a universal answer to every security threat.
Where the flow breaks down
The biggest weakness is the possibility of losing the only device that can generate the codes. If you change phones without planning the move, the new installation may not automatically give you access to the old entries. That is why I would never treat the phone as the sole copy of my recovery strategy. Before replacing or resetting a device, I would review each account’s transfer or re-enrollment process and confirm that I can still sign in.
The app is also not the right choice for someone who wants a complete identity-security system in one place. It does not replace strong, unique passwords, account recovery planning, or careful device security. Users who expect automatic password filling, cross-device account synchronization, or a guided backup system may find a broader security product more suitable.
There is a further trade-off for shared accounts. If several people need access, placing the only second factor on one person’s phone creates a bottleneck. In that situation, a team-oriented authentication arrangement or a provider with multiple approved security methods may be better. The authenticator can still be useful for an individual account, but shared access requires planning beyond simply generating codes.
In-app purchases range from $9.99 to $124.99 per item, so I would pay attention to any optional upgrade screen before confirming a purchase. The basic appeal of the app is its free entry point, but users should decide whether any paid option addresses a real need rather than assuming every extra is necessary for ordinary code generation.
Who should use it and who should skip it
I would recommend it to Android users who want a straightforward way to add code-based two-factor authentication, especially if they already manage passwords elsewhere and do not want a full security suite. It is also a reasonable first step for someone moving beyond text messages and willing to save recovery details responsibly.
I would be more cautious about recommending it to people who frequently replace phones, share account access with several people, or need advanced enterprise controls. Those users should first prioritize a clear migration process and a backup method. If those requirements are more important than having a focused, free authenticator, another type of security tool may fit better.
My final take after following the workflow
Authenticator App - 2FA succeeds when I judge it by the job it is meant to do: keep the temporary verification step close at hand and make code-based sign-ins practical. The complete journey is understandable, from opening an account’s security settings to adding the setup key, confirming the first code, and using it during a later login.
Its limitations are equally clear. The app does not remove the need for recovery planning, careful account labeling, or a sensible phone-change procedure. Those details determine whether two-factor authentication feels reassuring or becomes a source of lockouts. My strongest recommendation is to test the setup immediately and protect the recovery route before relying on the app.
With that preparation, I see this as a useful productivity companion rather than a complete security solution. It is free to begin, supports older Android devices from version 7.0 onward, and has enough reach to be familiar to many users. I would choose it for personal accounts where I want a dedicated code generator without a larger password-management system. I would look elsewhere when synchronization, shared administration, or stronger hardware-based protection is the main priority.
Frequently Asked Questions
What is Authenticator App - 2FA, and how does it protect my accounts?
Authenticator App - 2FA generates temporary verification codes that provide an extra layer of security when you sign in to supported online accounts. After entering your password, you also enter the code shown in the app. These codes usually change every few seconds, making it much harder for someone to access your account with a stolen or guessed password alone.
Which online services can I use with Authenticator App - 2FA?
The app generally works with services that support time-based one-time passwords, commonly called TOTP or authenticator-app verification. This may include email accounts, social networks, cloud platforms, cryptocurrency services, shopping websites, and many other apps. Compatibility depends on the individual service, so check its security settings for a QR code or setup key before adding an account.
Can I use Authenticator App - 2FA without an internet connection?
In most cases, yes. Once an account has been added, the app can generate time-based security codes directly on your device without requiring mobile data or Wi-Fi. Your phone’s clock must be reasonably accurate because the codes depend on synchronized time. Internet access may still be needed when initially linking an account or completing certain provider-specific security steps.
What happens if I lose my phone or delete the app?
Losing your phone or removing the app can make account recovery difficult if you have not prepared a backup method. Before relying on the app, save the recovery or backup codes supplied by each online service and consider enabling another trusted sign-in option. Some versions may offer backup or transfer features, but availability and restoration steps can vary by device and app configuration.
Is Authenticator App - 2FA free, and does it collect personal information?
The app may be available as a free download, although some editions can include advertisements, optional purchases, or premium features. Privacy practices differ between developers and versions, so review the store listing and privacy policy before installing. Also remember that the app protects locally stored verification tokens; it does not automatically secure the accounts themselves without correctly configured two-factor authentication.


